The Enterprise Creator Era: 2 Deadly Traps (Failed Security Tests & Token Bleed) and How Joget + Token Factory Solve Them
Author: AuthorWise Enterprise Technology & Architecture Strategy Team
Categories: AI Governance, Low-Code Platform, Enterprise Architecture, AI FinOps
Target Audience: CIOs, CTOs, IT Directors, Enterprise Architects, Heads of Digital Transformation, Innovation Leads
In the past, whenever marketing needed a campaign approval system, procurement requested vendor evaluations, or HR wanted an AI resume screening tool, they had to submit formal IT service tickets. What followed was almost always an agonizing 6 to 12-month IT backlog, often causing business opportunities to wither before a single line of code was written.
Today, business operations have entered "The Golden Era of Enterprise Creators"...
The convergence of Low-Code / No-Code platforms, Vibe Composition, and AI Copilots has empowered business employees—from financial analysts to operations managers—to become Citizen Developers and App Creators. They can assemble apps, automate multi-step approval workflows, and integrate AI into daily operations in days or even hours.
While this decentralized agility looks like an undeniable triumph, IT leaders and CFOs are quietly confronting a serious behind-the-scenes nightmare: two ticking time bombs that can abruptly derail enterprise digital transformation.
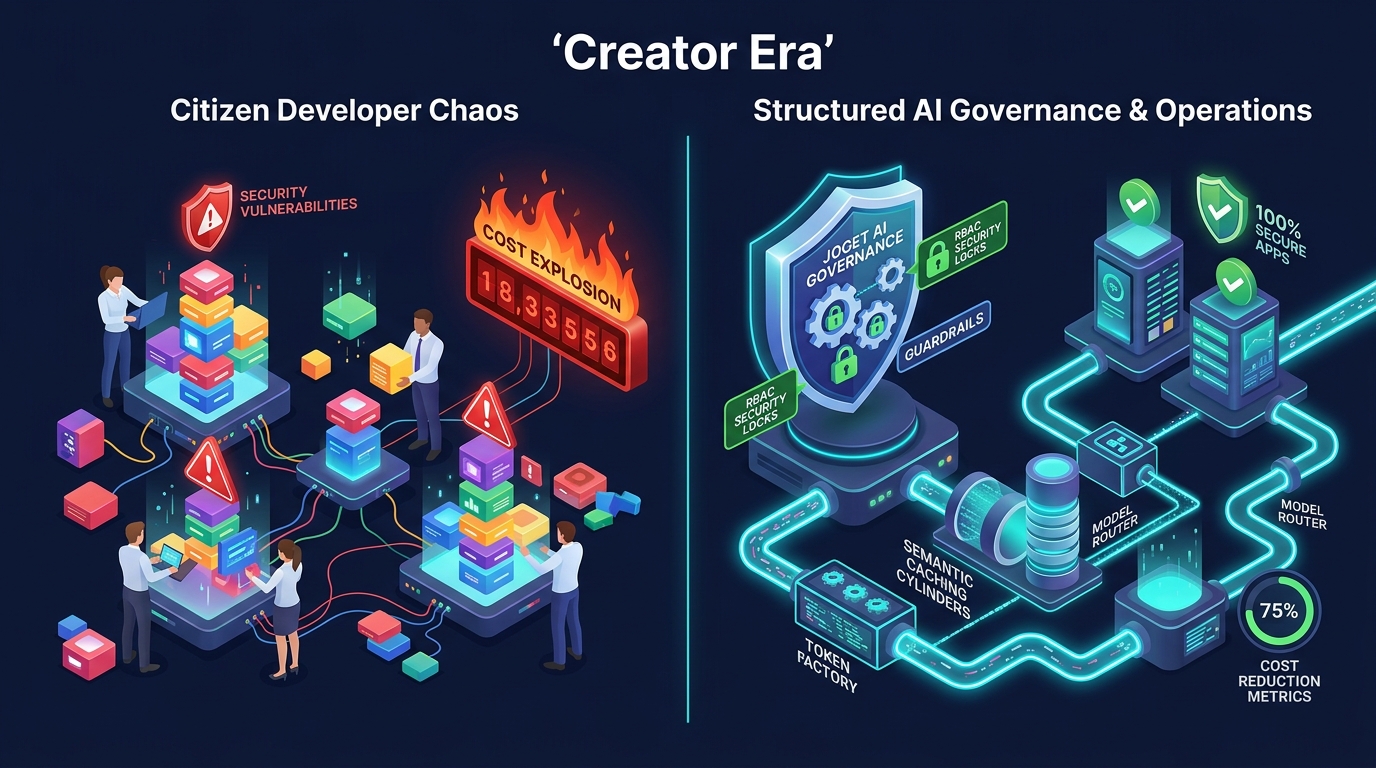
Figure 1: Citizen developer sprawl and token explosion (left) vs. structured enterprise security with Joget AI Governance and Enterprise Token Factory (right).
⚠️ 2 Critical Pitfalls of Ungoverned Enterprise App Creation
When non-engineers build apps without security guardrails and architectural cost controls, the hidden liabilities quickly overshadow initial excitement:
Trap 1: Lightning-Fast Development... But "100% Security Test Failure" (The Security Debt Trap)
Most business creators are domain experts in marketing, sales, or logistics, but they are not cybersecurity professionals. When creating apps or asking AI to generate scripts, they prioritize getting things to work while ignoring foundational security principles:
- Hardcoded API Keys & Database Secrets:
Creators frequently embed OpenAI API keys, Claude bearer tokens, or internal database connection strings directly into client-side scripts, where anyone in the department can inspect them. - Broken Role-Based Access Control (Broken RBAC):
Ad-hoc apps rarely enforce granular permissions. Any user opening the application can view unmasked payroll numbers, proprietary client data, or supplier pricing. - Severe PDPA & Corporate Data Leaks:
To summarize documents, employees often copy-paste personally identifiable information (PII) or confidential contracts straight into public commercial LLMs without data masking or token sanitization.
The Painful Consequence: When the application faces enterprise security compliance or external Penetration Testing (Pen-Test), it fails catastrophically on Day 1. Cybersecurity teams must immediately shut down the tool, reducing weeks of creative effort and employee enthusiasm into useless, abandoned digital waste.
Trap 2: Proliferating Apps with "Massive Token Bleed and Minimal Business ROI" (Token Burnout)
With easy AI API integration, companies suffer from "App Sprawl": dozens of departmental bots and automated workflows run unchecked, with no centralized metering:
- Overpowered Model Allocation ("Using a Sledgehammer to Crack a Nut"):
Trivial tasks like three-sentence text summarization or sentiment classification are wired directly to top-tier flagship LLMs (like GPT-4o or Claude 3.5 Sonnet) on every transaction, multiplying costs by 10x to 20x. - Zero Semantic Caching:
Fifty different employees asking identical questions about travel expense policies trigger fifty independent, billable API calls to commercial cloud providers. - Zombie Apps & Unmonitored Cron Loops:
Experimental workflows that creators abandoned continue triggering hourly webhooks and API loops in the background 24/7, continuously burning corporate funds.
The Painful Consequence: At month's end, the CFO and CIO face "Surprise Billing Shock"—API bills skyrocket into six-figure sums. Yet when evaluating business productivity gains, leadership discovers minimal tangible ROI, prompting executive leadership to freeze AI initiatives across the board.
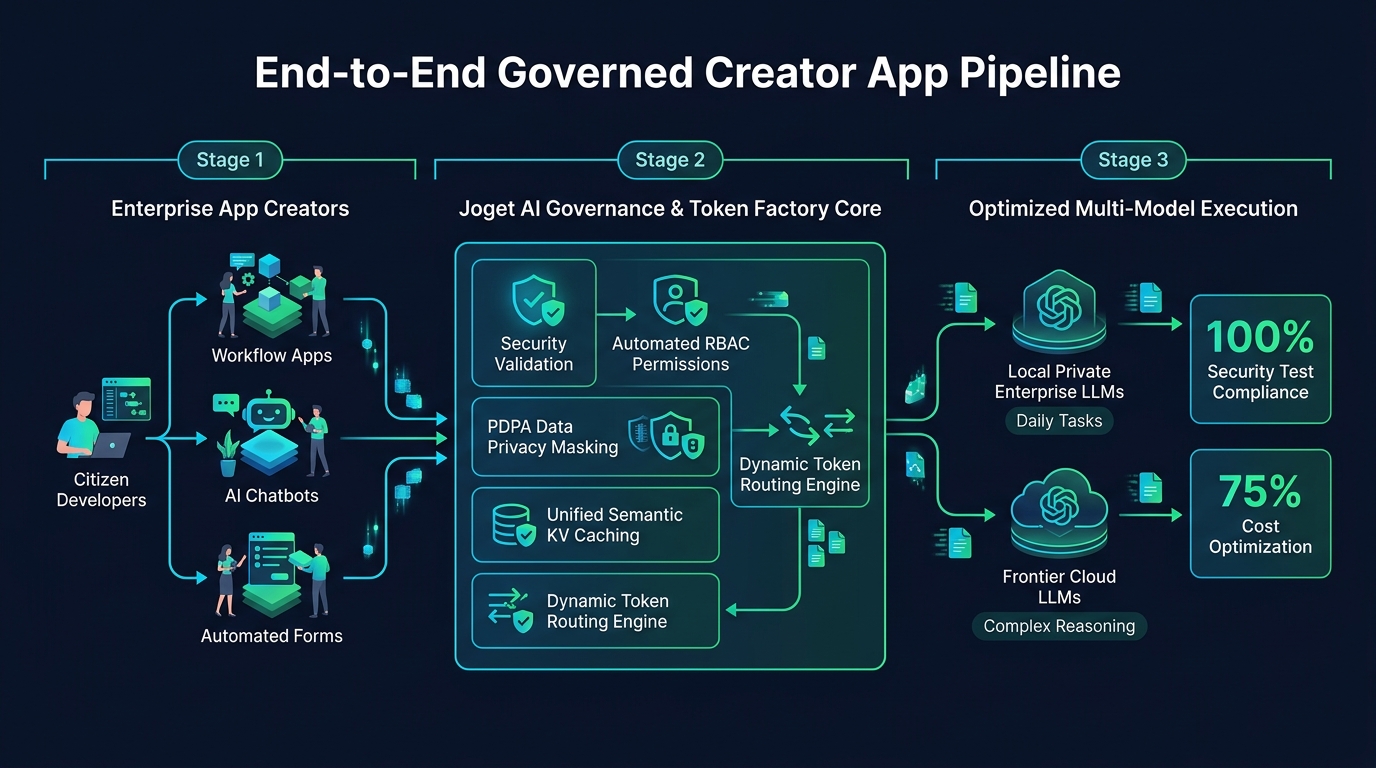 Figure 2: End-to-End governed pipeline routing creator apps through Joget AI Governance into the Enterprise Token Factory, achieving 100% security compliance and 75% cost savings.
🛠️ The Enterprise Solution: Joget DX (AI Governance) + Token Factory
The answer is never to ban employees from building apps—doing so suffocates competitive agility. Instead, enterprises must provide a "Governed Sandbox with Centralized Metering" by combining two core pillars:
1. Joget DX: Enterprise Low-Code with Built-in AI Governance (Secure by Design)
Joget DX is a world-class open-source enterprise Low-Code platform that enables citizen developers to build safely within robust architectural boundaries:
- From Fragile Code to "Vibe Composition":
Instead of writing raw, untested scripts, creators assemble business logic from enterprise-approved UI widgets, secure form components, and certified connectors. - Native Enterprise RBAC & Single Sign-On (SSO):
Seamlessly ties into Active Directory, Okta, and corporate IAM. Data access, edit rights, and multi-tier approval stages are strictly governed per user role and department. - AI Governance Guardrails & Data Privacy Filtering:
Joget actively intercepts prompts, sanitizing sensitive corporate data and PII before forwarding requests to AI models, while logging comprehensive audit trails for regulatory compliance. - 100% Pass Rate on Enterprise Security Tests:
Because applications inherit Joget’s hardened core architecture, they meet rigorous IT compliance, OWASP standards, and internal penetration tests on Day 1.
2. Enterprise Token Factory: Centralized Cost Control & Dynamic Smart Routing
With security guaranteed at the application layer, the Enterprise Token Factory serves as the central intelligent proxy and financial guardrail:
- Unified Control Plane & Departmental Quotas:
No individual creator app holds direct API keys. All calls pass through the Token Factory, enabling IT to enforce hard monthly budget caps per department and eliminate billing surprises. - Semantic KV Caching (Slash Redundant Costs by 60–80%):
Common queries and repetitive prompt patterns are intercepted and fulfilled immediately from the semantic cache without billing external LLM vendors. - Smart Model Routing (Right Task to the Right Model):
Evaluates query complexity dynamically: simple extraction or categorization tasks are routed to high-speed Internal Local LLMs or cost-effective models (such as Gemini Flash or GPT-4o-mini), while complex multi-step reasoning is directed to premium flagship models. - Dynamic Re-routing & Automatic Failover:
If a primary cloud API provider experiences downtime, latency spikes, or pricing shifts, the Token Factory automatically re-routes traffic to an equivalent, cost-optimal secondary model without disrupting creator workflows.
📊 Comparison Matrix: Ungoverned Creator Apps vs. Governed Architecture
| Evaluation Dimension | Ungoverned Creator Apps (Shadow IT) | Governed with Joget + Token Factory |
|---|---|---|
| Security & Compliance | ❌ High Risk: Hardcoded keys, data breach, fails security tests 100% | ✅ Maximum Security: Enterprise RBAC, sandboxed execution, 100% secure |
| Data Governance | ❌ Shadow IT: Disjointed apps, no audit trail, severe PDPA risks | ✅ Fully Auditable: Full transaction logs, native Single Sign-On (SSO) |
| Token Utilization | ❌ Wasteful: Flagship models called blindly, zero caching | ✅ Optimal Efficiency: Smart Routing + Semantic Caching saves up to 75% |
| Budget Management | ❌ Billing Shock: Month-end budget explosion, runaway expenses | ✅ Strict Control: Departmental budget caps & real-time quota metering |
| Operational Resilience | ❌ Fragile: Third-party cloud API outage breaks all apps instantly | ✅ High Resilience: Dynamic re-routing and seamless local model fallback |
| Enterprise Business ROI | ❌ Low ROI: High spend, unverified impact, risk of immediate shutdown | ✅ Measurable ROI: Rapid, secure innovation with proven business value |
🚀 How AuthorWise Empowers Your Enterprise
Digital transformation should never throttle employee creativity—it must provide a "high-speed, bulletproof railway" on which creator innovation can run smoothly and securely.
As your Enterprise AI Implementation & Governance Partner, AuthorWise provides:
- Joget DX Enterprise Deployment & Enablement:
Certified partner services in Thailand, offering low-code architecture setup, workflow modeling, and Citizen Developer Academy training programs. - Enterprise Token Factory & AI Gateway Architecture:
End-to-End design connecting hybrid infrastructure (Local LLMs + Cloud APIs), configuring Semantic Caching, and deploying real-time FinOps monitoring dashboards. - AI Security & Governance Assessment:
Comprehensive audits of internal departmental applications to ensure rigorous compliance with cybersecurity guidelines and data privacy regulations.
💡 Ready to empower your enterprise creators with 100% security compliance and 75% token cost optimization?
Consult with AuthorWise specialists today:
📞 Tel: +66-81-555-6615
✉️ Email: auttakorn.ph@authorwise.co.th
🌐 Website: www.authorwise.co.th